

The GDPR : as soon as personal data is processed
An AI agent that reads accident reports, certifications, or fitness-for-work assessments processes personal data, often health data, which is strictly regulated by Article 9 of the GDPR.
Key points to watch :
- purpose and minimization : the agent only accesses data necessary for its task ;
- automated decision-making : Article 22 of the GDPR protects individuals against decisions based solely on automated processing that produce significant effects. Human validation is therefore essential for any decision concerning an employee ;
- security and hosting : where is the data processed, by whom, and is it being reused to train a model ?
The CNIL publishes practical guides on AI that detail these points. For the hosting aspect, see QHSE AI and health data.
The AI Act : transparency and risk level
The Regulation (EU) 2024/1689 categorizes AI systems according to their risk level. Two points directly concern a conversational agent in QHSE.
Transparency
Article 50 stipulates that people interacting with an AI system must be informed of it. A conversational agent must therefore identify itself as such.
Risk level based on usage
An agent that helps draft a report or retrieve a document is not in the same category as a tool that evaluates or monitors workers. The regulation classifies certain systems used in the field of employment and worker management as high-risk. Classification is determined on a case-by-case basis.
The application dates have been adjusted by Regulation (EU) 2026/1744, known as the Digital Omnibus, particularly for high-risk systems. Check the updated schedule at EUR-Lex before making any decisions. Our article ISO 42001 and the AI Act covers these dates.
ISO 42001 : A voluntary governance framework
The ISO/IEC 42001 is an AI management system standard. It structures governance: policy, roles, risk management, impact assessment, internal audit, and continuous improvement. It is voluntary. To date, it is not a harmonized standard under the AI Act : applying it does not equate to a presumption of conformity. However, it demonstrates that a developer is organizing the control of their AI. See our ISO 42001 guide.
What you can demand from a provider
- Clear information when you are speaking to an AI.
- Clear human oversight : the agent proposes, a user validates.
- Clear documentation : operation, data used, limitations.
- Clear data policy : hosting, reuse, subcontractors.
- Clear AI governance structured, ideally according to a recognized framework.
The detailed list can be found in our 10 questions to ask your vendor.
Symalean's position
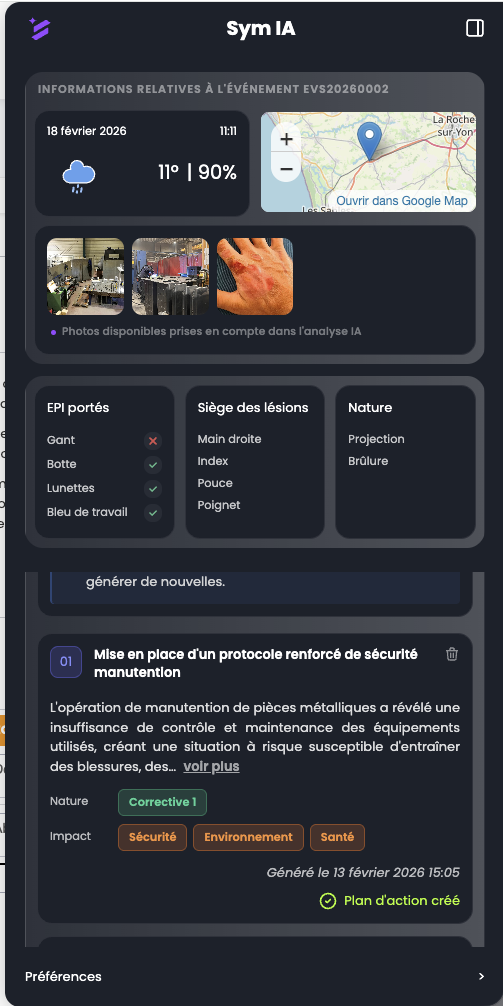
SymAI is Symalean's proprietary AI agent, developed by Symalean and hosted on HDS-certified servers. Symalean designs it in compliance with the GDPR and the AI Act framework, and has initiated an ISO/IEC 42001 certification process.